

7 Vulnerability Management Program Steps
Most companies do not fail at vulnerability scanning. They fail at decision-making after the scan. That is why vulnerability management program steps matter. If your team is collecting findings but still arguing over ownership, priorities, exceptions, and timelines, you do not have a mature program. You have a reporting problem.
A real vulnerability management program is not a weekly scan and a long backlog. It is a leadership discipline that connects asset visibility, risk tolerance, remediation, and governance. For executives, the goal is not more data. The goal is fewer material weaknesses, fewer preventable incidents, and a clear record that the business is managing cyber risk with intent.
Contents
The 7 vulnerability management program steps that matter
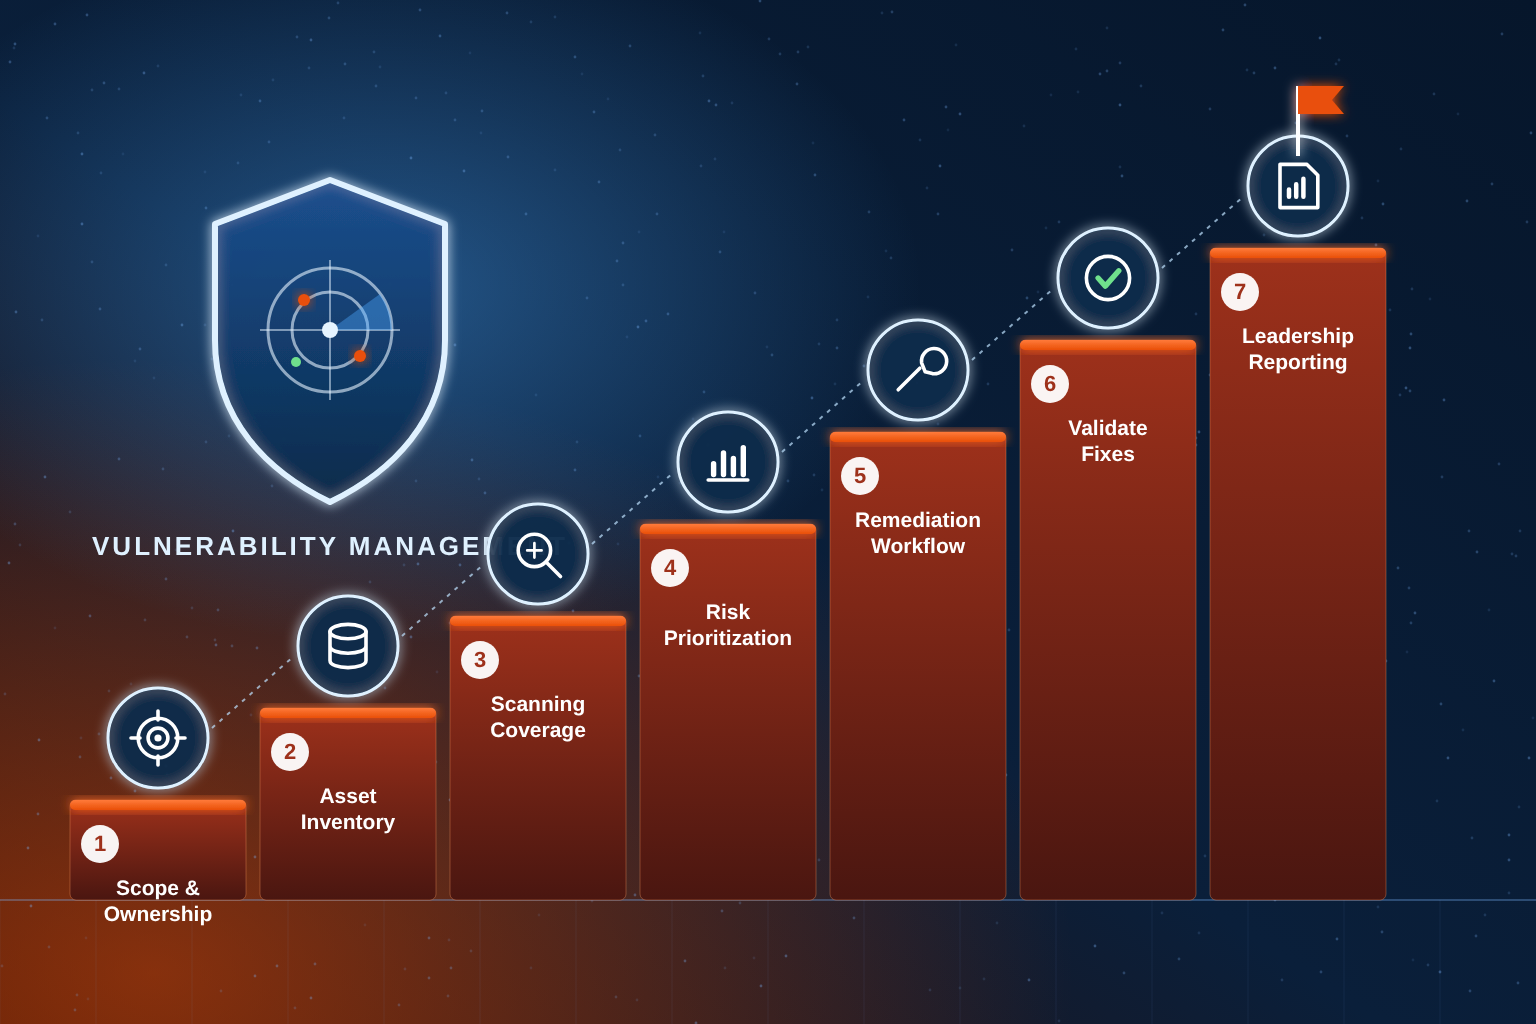
The right sequence keeps teams from wasting time on noise. The wrong sequence creates a flood of findings with no path to action. These seven steps give structure to the work and make it possible to measure progress.
The 7 Steps at a Glance
| Step | Focus | Key Output |
|---|---|---|
| 1. Define scope and ownership | Program charter, business owners | Agreed scope and named owners |
| 2. Build asset inventory | Cloud, endpoints, applications, vendors | Classified asset inventory |
| 3. Establish scanning coverage | Internal, external, cloud, web application, endpoint | Coverage based on exposure and impact |
| 4. Prioritize by risk | Exploitability and business impact | Risk-ranked findings |
| 5. Set remediation workflows | Owners, deadlines, exceptions | Due dates and approved exceptions |
| 6. Validate fixes | Rescanning, verification, residual risk | Verified closure and visible residual risk |
| 7. Report to leadership | Trend, exposure, accountability | Decision-ready business reporting |
Expert Insight
Vulnerability programs rarely fail at detection. They fail when nobody has the authority to decide what gets fixed, by when, and who accepts the risk that remains. Settling those decisions first makes every later step easier.
1. Define scope and business ownership first
Before you scan anything, decide what the program actually covers. That sounds obvious, but many organizations skip it. They start with tooling, then discover later that nobody agreed on which business units, cloud accounts, endpoints, applications, or vendors were in scope.
Start with the assets that support critical revenue, regulated data, operational continuity, and customer trust. Then assign business ownership, not just technical custody. IT may manage the server, but the application owner needs to understand the operational risk if it remains exposed.
This is also where leadership sets the program charter. What is the purpose of the program? Which risks are unacceptable? Which systems require stricter timelines? If there is no executive direction here, remediation turns into negotiation.
What to Define Before the First Scan
| Decision | Question to Answer | Who Decides |
|---|---|---|
| Scope | Which business units, cloud accounts, endpoints, applications, and vendors are covered? | Leadership with IT |
| Priority assets | Which assets support revenue, regulated data, continuity, and customer trust? | Business owners |
| Ownership | Who owns the operational risk, not just the technical custody? | Application and business owners |
| Program charter | What is the purpose, which risks are unacceptable, and which systems need stricter timelines? | Executive leadership |
2. Build an accurate asset inventory
You cannot manage vulnerabilities on assets you do not know exist. That is the most common structural weakness in mid-market environments. Cloud sprawl, shadow IT, remote devices, legacy systems, and unmanaged third parties create blind spots that no scanner can fix on its own.
Your inventory should classify assets by type, owner, environment, business criticality, internet exposure, and data sensitivity. This is what lets you answer the question that matters most: which vulnerabilities affect the systems the business actually depends on?
Perfection is not required on day one. Coverage improves over time. But if your inventory is weak, your metrics will be misleading and your remediation efforts will be uneven.
How to Classify Each Asset
| Attribute | Question It Answers |
|---|---|
| Type | What kind of asset is it? |
| Owner | Who is accountable for it? |
| Environment | Is it production, test, or development? |
| Business criticality | How much does the business depend on it? |
| Internet exposure | Can it be reached from the internet? |
| Data sensitivity | What data does it hold? |
3. Establish scanning and discovery coverage
Once scope and inventory are defined, scanning becomes useful. Internal scanning, external scanning, authenticated scans, cloud posture reviews, web application testing, and endpoint telemetry all have a place. The mix depends on your environment.
A small company with a limited stack may need straightforward network and endpoint coverage. A larger business with hybrid cloud, multiple subsidiaries, and customer-facing applications will need broader discovery and stronger validation. This is where many leaders overspend on tools and still underperform operationally.
Coverage should be based on exposure and business impact, not vendor promises. An externally exposed asset that handles customer data deserves tighter review than an isolated internal system with limited business value. The program should reflect those realities.
Scanning and Discovery Methods Compared
| Method | Best For | Watch Out For |
|---|---|---|
| Internal scanning | Servers, workstations, internal network | Isolated or unmanaged segments |
| External scanning | Internet-facing assets | Forgotten or unknown exposed assets |
| Authenticated scans | Deeper visibility into patches and configuration | Needs managed scan credentials |
| Cloud posture reviews | Cloud accounts and configurations | Cloud sprawl and shadow IT |
| Web application testing | Customer-facing applications | Findings that need stronger validation |
| Endpoint telemetry | Remote and roaming devices | Unmanaged devices |
How to turn findings into risk-based action
Finding vulnerabilities is the easy part. The harder part is deciding what gets fixed first, what gets accepted, and what needs compensating controls because remediation is not immediately possible.
4. Prioritize by exploitability and business impact
Severity scores are useful, but they are not enough. A critical vulnerability on an abandoned internal test system may be less urgent than a high-severity issue on an internet-facing production asset tied to revenue.
Effective prioritization combines technical severity with real-world context. Ask whether the asset is externally exposed, whether there is known exploitation in the wild, whether compensating controls already exist, and what the business impact would be if the asset were compromised.
This is where executive leadership changes the quality of the program. Security teams often know the threat. Business leaders know the consequence. You need both. A vulnerability management program that ignores business impact creates backlog theater instead of risk reduction.
Factors That Drive Risk-Based Prioritization
| Factor | Question to Ask | Effect on Priority |
|---|---|---|
| Technical severity | How severe is the vulnerability on paper? | Starting point, not the answer |
| Exploitation in the wild | Is there known exploitation? | Raises urgency |
| External exposure | Is the asset reachable from the internet? | Raises urgency |
| Compensating controls | Do controls already reduce the risk? | May lower urgency |
| Business impact | What happens if the asset is compromised? | Sets final priority |
Expert Recommendation
Pair every critical finding with a business owner who can describe the consequence of compromise. Technical severity tells you how serious a flaw is. The business owner tells you how much it would actually hurt.
5. Set remediation workflows, deadlines, and exceptions
A finding without an owner and a due date is just documentation. Mature programs define service levels for remediation based on asset criticality and vulnerability risk. They also define how exceptions are requested, approved, and reviewed.
For example, an actively exploited vulnerability on an internet-facing system may require remediation within days. A lower-risk issue on a segmented internal asset may reasonably wait for a scheduled maintenance window. The point is not to be rigid. The point is to be consistent and accountable.
Exception handling is where weak programs usually break down. Legacy applications, unsupported systems, operational constraints, and vendor dependencies are real. But exceptions should have an expiration date, documented rationale, named approver, and compensating controls where possible. Otherwise, temporary risk acceptance becomes permanent exposure.
Illustrative Remediation Expectations
| Scenario | Typical Expectation |
|---|---|
| Actively exploited vulnerability on an internet-facing system | Within days |
| High-risk finding on a business-critical asset | Defined service level based on asset criticality |
| Lower-risk issue on a segmented internal asset | Scheduled maintenance window |
What Every Exception Needs
| Required Element | Why It Matters |
|---|---|
| Expiration date | Stops temporary risk acceptance from becoming permanent exposure |
| Documented rationale | Records why remediation is not currently possible |
| Named approver | Creates clear accountability for the accepted risk |
| Compensating controls | Reduces exposure while the issue remains open |
Expert Insight
Track exception debt the way finance tracks financial debt: how many are open, how old they are, and who approved them. A growing exception list is an early warning that the program is losing control.
6. Validate fixes and measure residual risk
Closing a ticket is not the same as fixing the problem. Patches fail, configurations drift, and some vulnerabilities require more than one control change to eliminate the exposure.
Validation should include rescanning, targeted verification, and where appropriate, security testing that confirms the issue is no longer exploitable. This matters for audit readiness, but more importantly, it matters for trust in the program. If teams do not believe that closure data is accurate, they will stop trusting the metrics.
Residual risk should also be visible. Some systems cannot be fully remediated in the near term. In those cases, the program should show what risk remains, what compensating controls are in place, and when the issue will be reviewed again. That is a governance function, not just a technical one.
Validation Methods and Their Purpose
| Method | Purpose |
|---|---|
| Rescanning | Confirms the vulnerability no longer appears |
| Targeted verification | Confirms the specific patch or configuration change worked |
| Security testing | Confirms the issue is no longer exploitable |
| Residual risk record | Shows remaining risk, compensating controls, and the next review date |
7. Report to leadership in business terms
The final step in vulnerability management program steps is the one that determines whether the program survives budget scrutiny. Leadership reporting must show trend, exposure, accountability, and decision points.
Do not lead with raw vulnerability counts. They rarely help. A better report shows how many critical assets are covered, how quickly high-risk findings are remediated, where recurring failures exist, which exceptions remain open, and whether the organization is reducing risk in its most important environments.
Boards and executives do not need a scanner export. They need a clear view of whether cyber risk is being controlled, where investment is needed, and which business owners are carrying unresolved exposure. That shift from technical output to management insight is what separates a tool-led effort from a real program.
From Technical Output to Management Insight
| Instead of Reporting | Report |
|---|---|
| Raw vulnerability counts | How many critical assets are covered |
| Total open findings | How quickly high-risk findings are remediated |
| Scanner exports | Where recurring failures exist |
| Ticket volume | Which exceptions remain open and who owns them |
| Technical output | Whether risk is falling in the most important environments |
Where vulnerability programs usually stall
The biggest problem is not lack of tools. It is fragmented accountability. Security identifies issues, infrastructure owns some of them, application teams own others, and nobody owns the full process. That is why leadership matters.
The second problem is overreliance on severity scores. Teams chase CVSS numbers while missing exploitability, exposure, and operational importance. The result is predictable: large backlogs, slow remediation, and no confidence that the right problems are being solved first.
The third problem is treating vulnerability management as a purely technical task. It is not. It sits at the intersection of operations, governance, compliance, and risk management. A mature program supports regulatory obligations, strengthens customer assurance, and improves resilience during incidents.
For growing businesses, this is often the point where outside leadership makes the difference. A structured advisory model, such as the kind CISOLead provides, can establish ownership, reporting discipline, and executive alignment without forcing the company to build a full in-house security leadership function overnight.
Common Stall Points and How Leadership Resolves Them
| Problem | Symptom | Leadership Fix |
|---|---|---|
| Fragmented accountability | Nobody owns the full process | Assign clear end-to-end ownership |
| Overreliance on severity scores | Large backlogs and slow remediation | Add exploitability, exposure, and operational importance |
| Treated as a purely technical task | Disconnected from governance and compliance | Connect it to operations, governance, compliance, and risk management |
What good looks like after 90 days
A credible program does not need to be perfect. It needs to be controlled. After the first 90 days, most organizations should be able to show defined scope, baseline asset visibility, regular scanning coverage, risk-based prioritization, documented remediation timelines, an exception process, and leadership reporting that supports decisions.
90-Day Maturity Checkpoints
| Checkpoint | What You Should Be Able to Show |
|---|---|
| Defined scope | Agreed coverage with named business owners |
| Baseline asset visibility | A classified inventory of the systems that matter most |
| Regular scanning coverage | Scans aligned to exposure and business impact |
| Risk-based prioritization | Findings ranked by exploitability and business impact |
| Documented remediation timelines | Due dates and owners for every finding |
| Exception process | Requested, approved, and reviewed exceptions |
| Leadership reporting | Reports that support decisions |
From there, maturity grows through consistency. Coverage improves. Metrics get cleaner. Exception debt goes down. Business owners become more accountable. Security becomes less reactive because the organization has a repeatable process instead of a recurring scramble.
That is the real value of a vulnerability management program. It gives the business a disciplined way to reduce preventable exposure without pretending every finding carries the same weight. Strong security leadership knows the difference between activity and control. Your program should too.
If your current process produces more tickets than decisions, start there. Tighten ownership, sharpen prioritization, and make risk visible in business terms. That is how vulnerability management starts delivering what leadership actually needs - fewer surprises and better control.
Expert Recommendation
A vulnerability program is ready for leadership when it can answer three questions on a single page: what is exposed, who owns it, and what is being done about it. If any of those answers is missing, fix the process before buying more tools.
FAQ
1. Why do most companies fail not at scanning, but at post‑scan decision-making?
Because scanning produces data, but ownership, prioritization, and timelines are missing. Without structure, the program becomes reporting—not risk reduction.
2. What are the 7 vulnerability management program steps that actually matter?
Define scope → build inventory → establish scanning coverage → prioritize by risk → set remediation workflows → validate fixes → report to leadership.
3. What does “risk‑based prioritization” mean in practice?
It means combining exploitability + business criticality + exposure, instead of chasing CVSS scores. This reduces real risk, not just ticket volume.

Alexander Boychev
Published on: June 23, 2026 | Last Updated: June 23, 2026Business Executive & Digital Marketing Manager at Advanced Vision IT
Alexander bridges technology, sales strategy, and strategic marketing, specializing in key account management, digital growth initiatives, and enterprise cloud and cybersecurity solutions. Find out more about me
ADVANCED VISION IT - MALTA
Address: Suite 8, Ta’ Mallia Buildings, Triq In‑Negozju, Zone 3, Central Business District, Birkirkara, CBD 3010, Malta
Registration number: C111282, VAT Number: MT31713827
Phone:+35679224404
Email: office@advisionit.com
ADVANCED VISION IT - BULGARIA
Address: 35 Dimitar Hadzhikotsev str. Ent A, Lozenets, Sofia, Bulgaria
ID No: 205789039, VAT No: BG205789039
Phone: +359 888 258 530
Email: office@advisionit.com