

7 Best Cyber Risk Dashboards That Matter
Most organizations are not short on security data. They are short on clarity. The best cyber risk dashboards are not designed to impress analysts. They are designed to help executives, boards, and operational leaders make informed decisions faster.
If your dashboard needs a security analyst standing next to it to explain what it means, it is not doing its job. The best cyber risk dashboards do one thing well: they help leaders make decisions faster. They do not dump controls, alerts, and technical noise onto a screen. They translate cyber exposure into business risk, operational priorities, and executive action.
That distinction matters. Most organizations are not short on data. They are short on clarity. Security tools generate thousands of events, but boards, CEOs, and operating leaders need to know something simpler: where the business is exposed, how serious that exposure is, and what needs funding or attention now.
Contents
- What the best cyber risk dashboards actually do
- 7 best cyber risk dashboards for executive use
- Dashboard comparison
- What separates good dashboards from bad ones
- The metrics worth putting on a cyber risk dashboard
- Common mistakes when choosing cyber risk dashboards
- How to build a dashboard leadership will actually use
- FAQ
What the Best Cyber Risk Dashboards Actually Do
A useful cyber risk dashboard is not a prettier SIEM view. It is a management tool. It should help executives, IT leaders, compliance owners, and security teams align on the same facts without forcing everyone into the same level of detail.
The best cyber risk dashboards usually connect five ideas in one place: threat exposure, control effectiveness, business impact, compliance position, and action status. If one of those is missing, the picture gets distorted. A dashboard that shows vulnerabilities without business criticality creates panic. A dashboard that shows compliance status without actual exposure creates false confidence.
Expert Insight
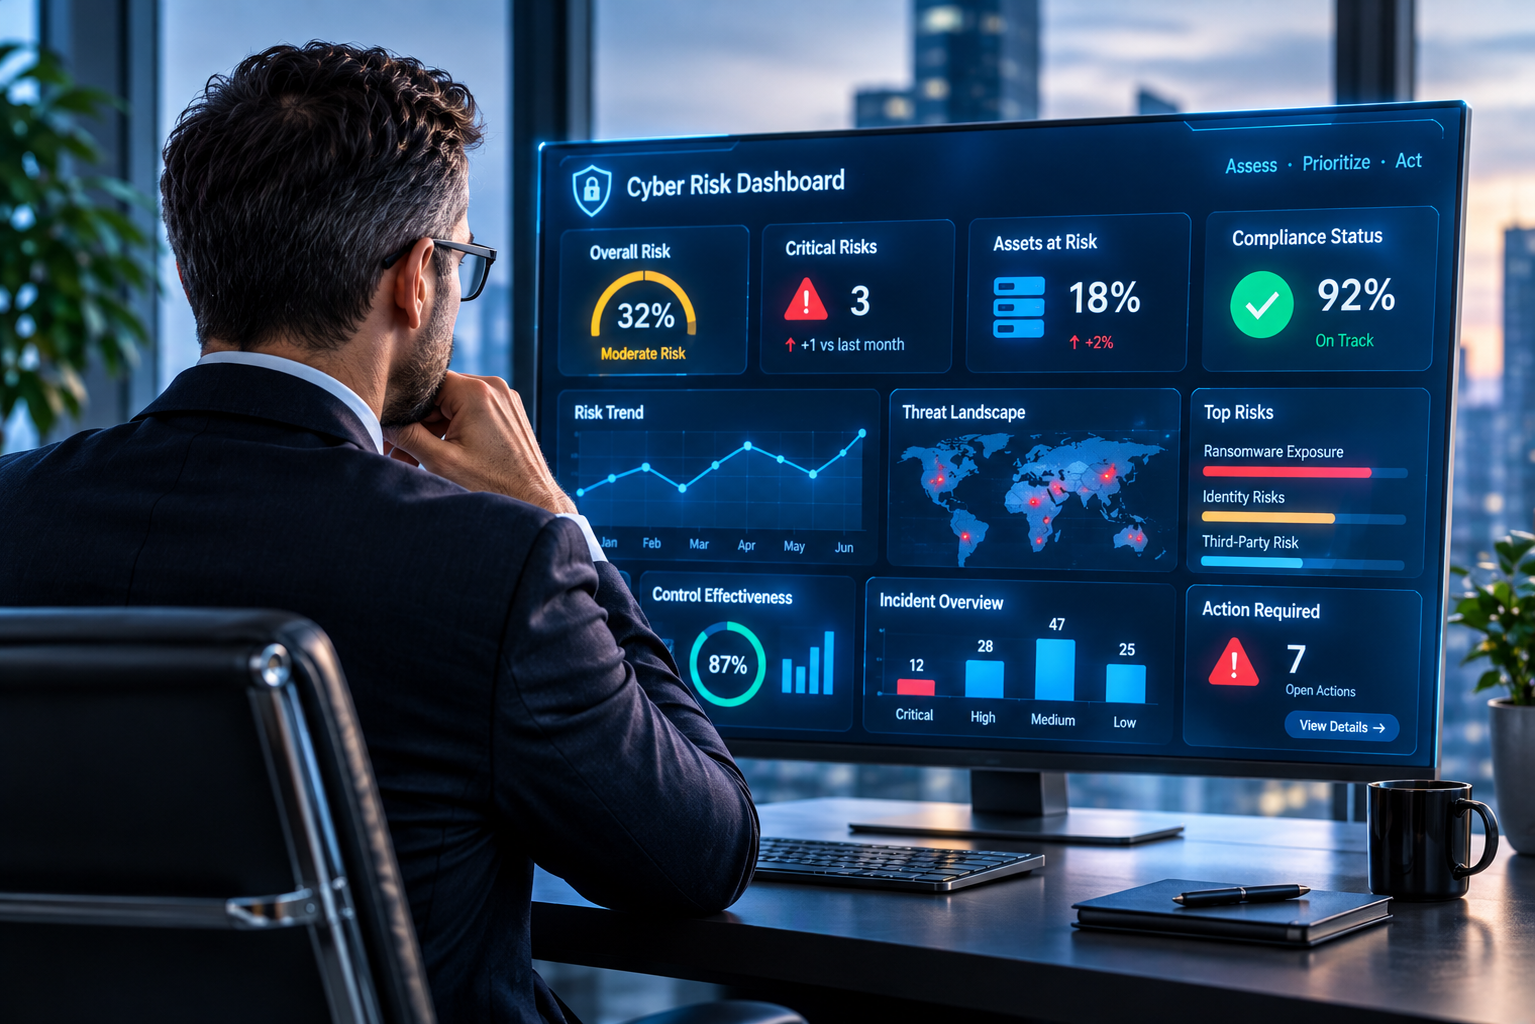
The primary purpose of a cyber risk dashboard is not visibility. It is decision-making. The most effective dashboards answer three executive questions immediately: What is exposed? What changed? What action is required?
7 Best Cyber Risk Dashboards for Executive Use
There is no single universal dashboard. The right model depends on your maturity, reporting structure, and regulatory pressure. But seven dashboard types consistently create value when they are built correctly.
1. Executive Cyber Risk Dashboard
This is the boardroom version. It should be concise, business-aligned, and free of technical clutter. Think enterprise risk levels, top material risks, trend direction, open decisions, and mitigation status.
The audience here does not need CVE counts by asset group. They need to understand whether ransomware exposure is rising, whether identity controls are improving, and whether unresolved risks could affect revenue, operations, or compliance. A good executive dashboard also shows ownership. Risk without an accountable leader is just a slide.
This is where many teams get stuck. They build for visibility instead of decision-making. Visibility is useful, but leadership requires prioritization. A dashboard earns its place when it helps answer questions like: Are we reducing material risk? Which business units are carrying the most exposure? Where are we out of policy? What needs executive sponsorship?
2. Vulnerability and Exposure Dashboard
This dashboard helps security and IT leadership separate noise from actual exposure. It should prioritize assets by business criticality, internet exposure, exploitability, and remediation age.
A raw patch count is a weak metric. It can make a team look productive while critical systems remain exposed. The stronger version shows high-risk vulnerabilities on crown-jewel assets, exceptions that have aged beyond policy, and whether remediation is improving where it matters most.
3. Identity and Access Risk Dashboard
Most serious breaches involve identity somewhere in the chain. This dashboard should focus on privileged access, MFA coverage, dormant accounts, risky third-party access, and policy exceptions.
For many organizations, this becomes one of the most valuable views because identity sits at the center of both security and operations. If executives can see that privileged access has grown faster than governance, that is a leadership issue, not just an IT issue.
Dashboard Types and Their Primary Business Value
| Dashboard Type | Primary Audience | Business Value |
|---|---|---|
| Executive Risk | Board & Executives | Strategic decisions |
| Vulnerability & Exposure | IT & Security Leaders | Exposure reduction |
| Identity Risk | Security Leadership | Access governance |
| SOC Effectiveness | Operations Teams | Incident response performance |
| Third-Party Risk | Risk & Procurement | Vendor oversight |
| Compliance & Governance | Compliance Teams | Audit readiness |
| Cyber Resilience | Executive Leadership | Business continuity |
4. Security Operations Effectiveness Dashboard
This one is often overbuilt. Keep it centered on outcomes. Mean time to detect and respond still matters, but only when paired with incident severity, containment success, and repeat issues.
If your SOC closes alerts quickly but major incidents still escalate, the dashboard should make that obvious. Speed alone is not performance. Effective dashboards show whether detection is improving against meaningful threats and whether response actions reduce recurrence.
5. Third-Party and Supply Chain Risk Dashboard
Vendors extend your attack surface whether you planned for it or not. A practical third-party dashboard should track critical vendors, assessment completion, unresolved findings, contract control gaps, and concentration risk.
This becomes especially important for growing companies that outsource key functions without mature governance.
6. Compliance and Governance Dashboard
Compliance does not equal security, but it does affect legal exposure, audit readiness, and customer trust. This dashboard should map obligations to current status, control ownership, evidence readiness, policy exceptions, and overdue actions.
The best version avoids vanity percentages. Saying you are 87 percent aligned with a framework tells leadership almost nothing. What matters is where you are noncompliant, whether the gap is tied to a real operational risk, and who is responsible for closing it.
7. Cyber Resilience Dashboard
This is the dashboard many companies need before they realize it. It focuses on recovery capability, backup integrity, incident readiness, tabletop exercise outcomes, and dependency risks across critical services.
A business can look secure on paper and still fail under pressure. Resilience metrics force a harder conversation: if key systems go down tomorrow, how quickly can we restore operations, and where will the recovery plan break first?
Expert Recommendation
Organizations often focus heavily on vulnerability and compliance reporting while overlooking resilience. Recovery capability, dependency management, and incident readiness are often stronger indicators of real-world business survivability than compliance percentages alone.
Cyber Risk Dashboard Maturity Comparison
| Dashboard Characteristic | Immature Reporting | Mature Risk Dashboard |
|---|---|---|
| Primary Focus | Tool data | Business decisions |
| Metrics | Volume-based | Risk-based |
| Audience | Security team only | Executives, security, compliance, IT |
| Reporting Style | Technical output | Business impact |
| Outcome | Awareness | Action |
What Separates Good Dashboards From Bad Ones
The difference is rarely visual design. It is governance.
Bad dashboards start with available tool data and stop there. Good dashboards start with leadership questions and work backward. They define the decisions the dashboard is meant to support, then select metrics that help answer those decisions clearly.
They also resist metric inflation. More tiles do not create more insight. A dashboard with 25 indicators usually hides the three that matter most. Executive reporting should show a risk position, trend, exception, and next action. Everything else can live in supporting views.
Context matters just as much as metrics. A rise in vulnerabilities may not be bad if asset coverage expanded after a new discovery effort. A drop in incidents may not be good if logging failed. Numbers without narrative create false certainty.
Expert Insight
A dashboard should never be evaluated by how much information it contains. It should be evaluated by how quickly a leadership team can make a risk decision after reviewing it.
The Metrics Worth Putting on a Cyber Risk Dashboard
If you are building or cleaning up a dashboard, focus on metrics that link security activity to business exposure. That usually includes inherent versus residual risk, critical asset exposure, control coverage on high-value systems, remediation age for severe issues, privileged access trends, phishing or identity-related incident patterns, third-party exceptions, and recovery readiness.
Not every organization needs all of these in the same place. A heavily regulated healthcare business may emphasize compliance gaps and resilience. A SaaS company may focus more on identity, cloud exposure, and vendor concentration. It depends on your operating model and what failure would actually cost the business.
Metrics That Matter Most to Leadership
| Metric | Business Question It Answers |
|---|---|
| Critical Asset Exposure | Which key systems are most at risk? |
| Residual Risk | Which risks remain after controls are applied? |
| Remediation Age | How long have major issues remained unresolved? |
| Privileged Access Trends | Is administrative access growing faster than governance? |
| Third-Party Exceptions | Where do vendors create unmanaged exposure? |
| Recovery Readiness | How prepared is the business to recover? |
Common Mistakes When Choosing the Best Cyber Risk Dashboards
- Buying a dashboard tool and expecting it to provide a cybersecurity strategy.
- Trying to serve executives, analysts, SOC teams, and auditors with a single view.
- Measuring activity instead of risk reduction.
- Focusing on vulnerability counts without business context.
- Ignoring ownership and accountability.
- Overloading dashboards with metrics that never drive decisions.
- Reporting compliance percentages without exposure metrics.
Expert Recommendation
One dashboard should support one type of decision. The moment a dashboard attempts to satisfy boards, analysts, auditors, IT operations, and security engineering simultaneously, its value drops dramatically.
How to Build a Dashboard Leadership Will Actually Use
Start with decisions, not data sources. Ask what your CEO, board, or operating leaders need to approve, fund, escalate, or accept. Then define the few measures that support those decisions.
Next, map every metric to an owner and a business process. If nobody owns a metric, it becomes decoration. If the metric cannot lead to action, it becomes trivia.
Then establish thresholds that mean something. Red, yellow, and green are useless unless they are tied to policy, appetite, or business impact. A red indicator should trigger a response, not a debate about formatting.
Finally, review the dashboard on a cadence that matches the risk. Monthly works for governance. Weekly may be necessary for exposure and response trends. The key is consistency. Dashboards become valuable when they shape recurring conversations, funding decisions, and accountability.
For many small and mid-sized businesses, this is exactly where outside leadership adds value. A service-led approach can connect technical telemetry, compliance obligations, and executive priorities into one reporting model instead of leaving IT to stitch together fragments.
The best cyber risk dashboards are not about making security look mature. They are about making risk visible enough to manage. If your dashboard cannot tell leadership what matters now, what changed, and what decision comes next, it is reporting activity, not leading security.
FAQ
1. What makes a cyber risk dashboard truly useful for leadership?
A useful dashboard translates technical data into business risk, priorities, and required actions. It should answer: “Where are we exposed? How serious is it? What needs funding or escalation now?”
2. What are the most valuable types of cyber risk dashboards?
Seven models consistently deliver value: executive risk, vulnerability & exposure, identity risk, SOC effectiveness, third‑party risk, compliance & governance, and cyber resilience.
3. What metrics should a strong cyber risk dashboard include?
Metrics that link security to business exposure: critical asset exposure, inherent vs residual risk, remediation age, privileged access trends, third‑party exceptions, and recovery readiness.
4. Why do many cyber risk dashboards fail?
Most fail because they measure activity instead of risk movement. Large volumes of alerts, closed tickets, and completed tasks do not automatically mean risk is decreasing.
5. How often should leadership review cyber risk dashboards?
Governance dashboards are typically reviewed monthly, while operational exposure and security operations dashboards may require weekly review depending on organizational risk and reporting requirements.

Alexander Boychev
Published on: June 22, 2026 | Last Updated: June 22, 2026Business Executive & Digital Marketing Manager at Advanced Vision IT
Alexander bridges technology, sales strategy, and strategic marketing, specializing in key account management, digital growth initiatives, and enterprise cloud and cybersecurity solutions. Find out more about me
ADVANCED VISION IT - MALTA
Address: Suite 8, Ta’ Mallia Buildings, Triq In‑Negozju, Zone 3, Central Business District, Birkirkara, CBD 3010, Malta
Registration number: C111282, VAT Number: MT31713827
Phone:+35679224404
Email: office@advisionit.com
ADVANCED VISION IT - BULGARIA
Address: 35 Dimitar Hadzhikotsev str. Ent A, Lozenets, Sofia, Bulgaria
ID No: 205789039, VAT No: BG205789039
Phone: +359 888 258 530
Email: office@advisionit.com